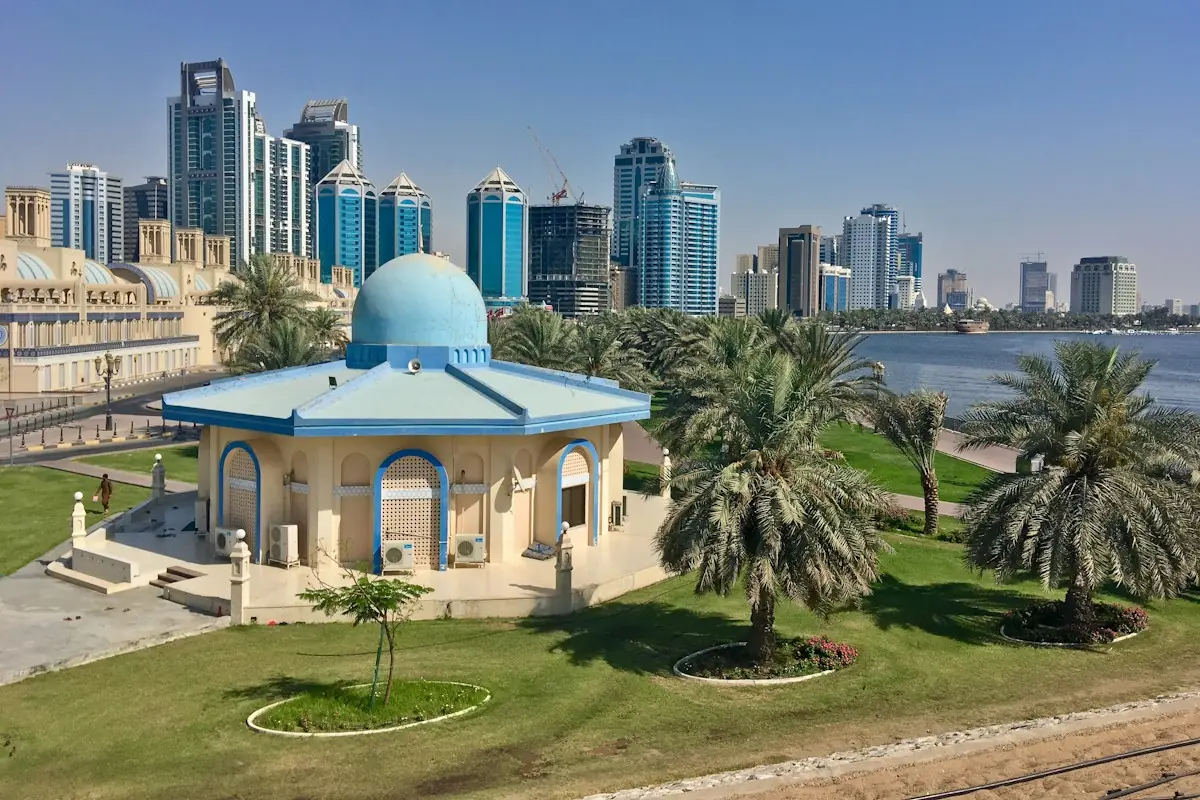
Sharjah city, SAIF Zone, Hamriyah, Shams and the industrial areas
VAPT & Penetration Testing in Sharjah
Intello provides VAPT services in Sharjah for manufacturers, logistics and trading companies, e-commerce businesses and growing SMEs. Our testers attack your web apps, networks and cloud the way a real attacker would, then give you a clear report, a fix plan and a retest.
- Minutes from Sharjah, in Al Qusais
- 500+ clients
- 99% client satisfaction
What is VAPT, and why Sharjah businesses need it
VAPT (vulnerability assessment and penetration testing) combines two checks. The vulnerability assessment finds known weaknesses across your systems. The penetration test then tries to exploit them by hand, to show which gaps are real and what an attacker could reach. For most Sharjah companies, the trigger is a client, bank, auditor or insurer asking for a recent test report.
| What we test | Web apps and APIs, external and internal networks, cloud (AWS, Azure, Google Cloud), people (phishing) and physical security |
|---|---|
| Approach | Manual testing on top of automated scanning, following OWASP and recognised testing methods |
| Typical length | 1 to 3 weeks of testing, depending on scope |
| You receive | An executive summary, a technical report with evidence, a risk-ranked fix plan and a retest report |
| Mapped to | PCI DSS, ISO 27001, SOC 2, the UAE PDPL and your client’s own security requirements |
| Where we work | From our office in Al Qusais, a few minutes from Sharjah, and remotely |
Penetration testing services across Sharjah
Sharjah runs on manufacturing, logistics, trade and a large base of small and mid-sized companies. Each needs a test scoped to what it actually exposes, and a report its clients will accept.
SAIF Zone
Logistics, trading and aviation-linked companies next to Sharjah Airport, with customer portals, shipment systems and remote access to test.
Hamriyah Free Zone
Oil and gas, steel and maritime suppliers whose international partners now ask for proof that their networks have been tested.
Sharjah Industrial Areas
Manufacturers whose ERP systems, supplier portals and remote access are a common way in for attackers.
Sharjah Media City (Shams)
E-commerce, media and start-ups with web apps and APIs that need testing before launch or for an investor.
Research, Technology and Innovation Park
Technology companies that need a test report for enterprise buyers, ISO 27001 or a SOC 2 audit.
Sharjah city and mainland
Retail, education, healthcare and professional services that take card payments or hold personal data under the UAE PDPL.
Also available: VAPT in Dubai · VAPT in Abu Dhabi · Cyber security company in Sharjah
Do you need a penetration test in Sharjah?
You almost certainly do if any of these apply to you:
- A client, multinational or bank has asked for a recent penetration test report
- You are working towards ISO 27001 or a SOC 2 audit
- You take card payments online or in store and must meet PCI DSS
- You are launching a new website, app or customer portal, or moving systems to the cloud
- You supply federal entities or critical sectors that follow the UAE IA Standard
- You have not had an independent security test in the last 12 months
Testing live systems? We agree testing windows and safe techniques with your team first, so production and day-to-day operations are not disrupted.
What our VAPT services in Sharjah cover
Each test is scoped to your systems and your reason for testing. These are the areas Sharjah companies ask for most.
Web application and API testing
Login, sessions, access control, injection and business-logic flaws, tested against the OWASP Top 10. More on web application penetration testing.
External network testing
Everything you expose to the internet: firewalls, VPNs, email, remote access and customer or supplier portals.
Internal network testing
What an attacker could do once inside: moving between systems, gaining admin rights and reaching sensitive data. See network penetration testing.
Cloud security testing
Misconfigured storage, over-broad permissions and exposed services in AWS, Azure and Google Cloud, including UAE cloud regions.
Physical security testing
Where it is in scope and authorised: building access controls, security procedures and the physical protection of devices.
Vulnerability assessment
Authenticated scanning of servers, endpoints and network devices, with false positives removed by hand so your team only fixes real issues.
Social engineering
Controlled phishing and phone tests, with your approval, to measure how staff respond.
Red team exercises
For mature teams: a goal-based attack over several weeks that tests detection and response. See red team services.
How a penetration test in Sharjah works
A fixed sequence, agreed in writing before any testing starts, so your systems and your operations stay safe.
- 1
Scoping call
We agree what is in scope, who the report is for, the testing window and any systems that must not be touched.
Day 0 · free
- 2
Rules of engagement
A signed authorisation, the test plan, IP ranges and test accounts. Live systems are tested only in agreed windows.
Before testing
- 3
Discovery and scanning
Reconnaissance and automated scanning to map the attack surface, then manual checks to remove false positives.
Week 1
- 4
Manual exploitation
Our testers exploit the real weaknesses and chain them together. Critical findings are flagged to you during testing, not held back for the report.
Weeks 1–2
- 5
Report and walkthrough
An executive summary, a technical report mapped to the framework you need, and a call to walk through every finding.
After testing
- 6
Retest
Once you have fixed the issues, we retest them and issue a retest report showing which findings are closed.
After your fixes
Web, API, cloud and external tests are usually remote. Internal tests are planned with your IT team, and our Al Qusais office is a few minutes from Sharjah for the kick-off and the walkthrough.
What our penetration testing services in Sharjah include
- Executive summary in plain language for management and owners
- Technical report with evidence and steps to reproduce each finding
- Risk rating for every finding (CVSS score plus business impact)
- Prioritised fix plan your IT team or developers can follow
- Mapping of findings to PCI DSS, ISO 27001 or SOC 2 where relevant
- A walkthrough call with the testers
- Retest report confirming which issues are closed
Choose your test
Vulnerability assessment
3–5 daysBest for: A fast, broad health check
- · Authenticated scanning
- · Manual validation
- · Risk-ranked report
Penetration test
1–3 weeksBest for: Client, audit and certification evidence
- · Manual exploitation
- · Report mapped to your framework
- · Retest of fixed findings
Yearly testing programme
Quarterly or yearlyBest for: Frequent releases and yearly audits
- · Scheduled tests
- · Testing after major changes
- · Year-round support
Has a client asked for your penetration test report?
Tell us what you need tested and by when. We send a written scope and a fixed quote.
Which frameworks expect penetration testing in Sharjah?
There is no Sharjah-only testing rule. These are the frameworks and client requirements that most often lead Sharjah companies to commission a penetration test.
| Framework | Who it applies to | What it expects |
|---|---|---|
| PCI DSS | Any business that takes card payments | Internal and external penetration tests at least every 12 months (PCI DSS requirement 11.4) |
| ISO 27001 | Companies certified for clients and tenders | Technical vulnerability management, usually evidenced by an independent test |
| SOC 2 | Software and service companies selling to US and global clients | Evidence that vulnerabilities are found and fixed, often a yearly penetration test |
| UAE PDPL | Any business processing personal data in the UAE | Appropriate technical measures to protect personal data, which testing helps prove |
| UAE IA Standard | Federal entities and critical-sector suppliers | Regular technical security testing of systems in scope |
What affects the cost of VAPT in Sharjah
Every quote is fixed and based on your scope. These are the factors that move the price:
- Number of targets
- How many web apps, APIs, IP addresses or cloud accounts are in scope.
- Application size
- The number of user roles, pages and API endpoints to test.
- Test type
- External only, internal, social engineering, or a full red team exercise.
- Sites
- Each office, warehouse or plant network in scope adds planning and testing time.
- Reporting needs
- Mapping to PCI DSS, ISO 27001, SOC 2 or a specific client’s requirements.
- Frequency
- A yearly or quarterly programme costs less per test than one-off tests.
Why businesses choose Intello as their penetration testing company in Sharjah
23+
years in UAE cybersecurity
500+
clients served
99%
client satisfaction
Manual testing, not just a scan. Every finding is checked by hand, so your team does not waste time on false positives.
Close by. Our Al Qusais office is minutes from Sharjah, so it is easy to meet in person for the kick-off and the walkthrough.
Reports your clients accept. Clear findings mapped to PCI DSS, ISO 27001, SOC 2 or your client’s own checklist.
We help you fix it. Remediation support and a retest, so the test ends with closed gaps, not just a PDF.
Frequently asked questions
How much do VAPT services in Sharjah cost?
It depends on scope: the number of applications, IP addresses, cloud accounts and user roles, whether internal or social engineering testing is included, and how many sites are involved. We give a fixed quote after a free scoping call, so there are no surprises.
Is penetration testing mandatory for Sharjah companies?
There is no Sharjah law that requires it for every company. It becomes required through the frameworks and contracts you sign up to: PCI DSS if you take card payments, ISO 27001 and SOC 2 audits, the UAE IA Standard for federal suppliers, and clients who ask for a recent report.
How often should a Sharjah business run a penetration test?
At least once a year, and after any major change such as a new website, app or customer portal, a cloud migration or a new office network. PCI DSS requires internal and external penetration testing at least every 12 months and after significant changes.
Will penetration testing disrupt our systems?
Testing is planned to avoid disruption. We agree testing windows, exclude fragile systems, avoid destructive techniques, and stop and contact you if we find something critical. Many companies prefer to test a staging copy of their website or app.
How long does a penetration test take?
Most web application or external network tests take one to two weeks of testing, and the report follows once testing is complete. Internal and red team engagements take longer. We agree the timeline in writing before we start.
What is the difference between VAPT and a vulnerability scan?
A scan is automated and lists possible weaknesses, including false positives. VAPT adds manual validation and exploitation by a tester, showing which weaknesses are real and what an attacker could reach. Clients and auditors expect a penetration test, not only a scan.
Can a small Sharjah company afford a penetration test?
Yes. A test scoped to what matters most, such as your website, customer portal or internet-facing systems, keeps the cost in proportion. A vulnerability assessment is a cheaper first step if you have never been tested.
How do I choose the best VAPT company in Sharjah?
Look for manual testing by qualified testers, a report your client or auditor will accept, a retest, clear fixed pricing and a team close enough to meet. Ask for a sample report before you decide.
Related services
Get a fixed quote for penetration testing in Sharjah
Tell us what you need tested. We will set up a short scoping call and send a written scope and quote.
What happens next
- 1We get in touch to arrange a call
- 2A 30-minute scoping call
- 3A written scope, timeline and fixed quote
Prefer to talk now? Call +971 55 355 6787